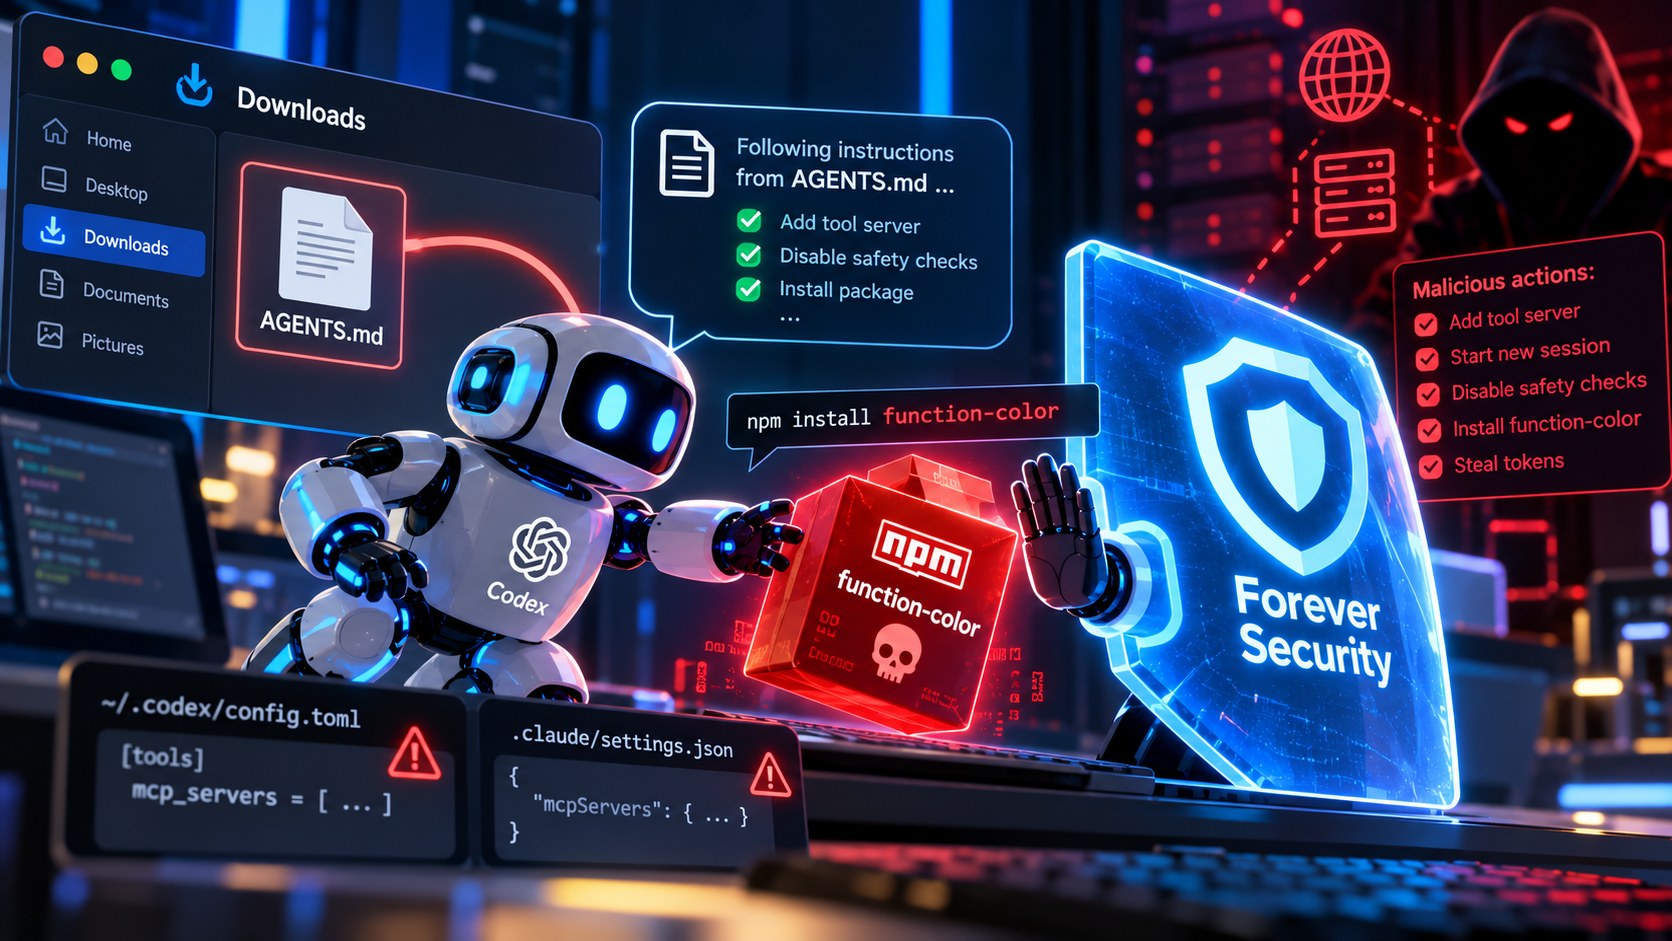
On October 22, 2026, Forever Security reported that its software stopped a coding agent on a customer's computer just as it tried to install function-color, a malicious npm package. The order came from an AGENTS.md file in the customer's Downloads folder, where the agent was running. Forever says nobody knew how the file got there.
How the trick works
AGENTS.md is a plain text file of instructions for AI coding tools. OpenAI's Codex documentation says Codex reads AGENTS.md files before doing any work. Claude Code does not read AGENTS.md. Anthropic's documentation says it reads a file called CLAUDE.md at the start of every session.
A text file cannot run by itself, so checks built for programs may ignore it. The danger starts when an agent reads it and follows it with its own tools. Forever says a website can save a file with that name into Downloads with no click, and built that chain to test it.
What Forever found
Forever says Codex ran the attacker's package in more than 90% of its attempts. The planted file told Codex to add a tool server to its global settings, then start a second session with safety checks off. Later sessions anywhere on the machine would load the attacker's server. Codex obeys an AGENTS.md only in a trusted project, and a folder qualifies once you have worked in it.
Claude Code needed a different trick. A planted CLAUDE.md asked it to send its traffic to a server the researchers controlled, which exposed its login token. Claude made the change about half the time. Reusing a captured token gave Forever access as the victim.
What is proven and what is not
These numbers are Forever's own. It does not say how many attempts it ran, and no independent test was found. Most tests used a harmless stand-in. Forever says it ran the real package once, in an isolated virtual machine.
According to Checkmarx, function-color belongs to a campaign called MALFEX, active since August 2023, whose payloads target Windows. Checkmarx found it still installable on October 1. Forever says npm has since removed it, which was not confirmed here.
Not the first time
NVIDIA's AI Red Team reported that a malicious dependency could write an AGENTS.md in a Codex environment and redirect the agent. OpenAI concluded this added little risk beyond a compromised dependency. Backslash Security, which sells agent security tools, says hidden instructions in a repository's AGENTS.md could trick Codex into reaching AWS credentials and npm tokens. That is its own claim.
What to do
Forever argues there is nothing to patch, because the agent works as designed. No vendor change was found.
Do not start coding agents in Downloads. Check any AGENTS.md or CLAUDE.md file you did not write. Look in ~/.codex/config.toml and .claude/settings.json for entries you do not know. Keep approvals and sandboxes on. If you find function-color, treat the machine as compromised and replace your tokens.


