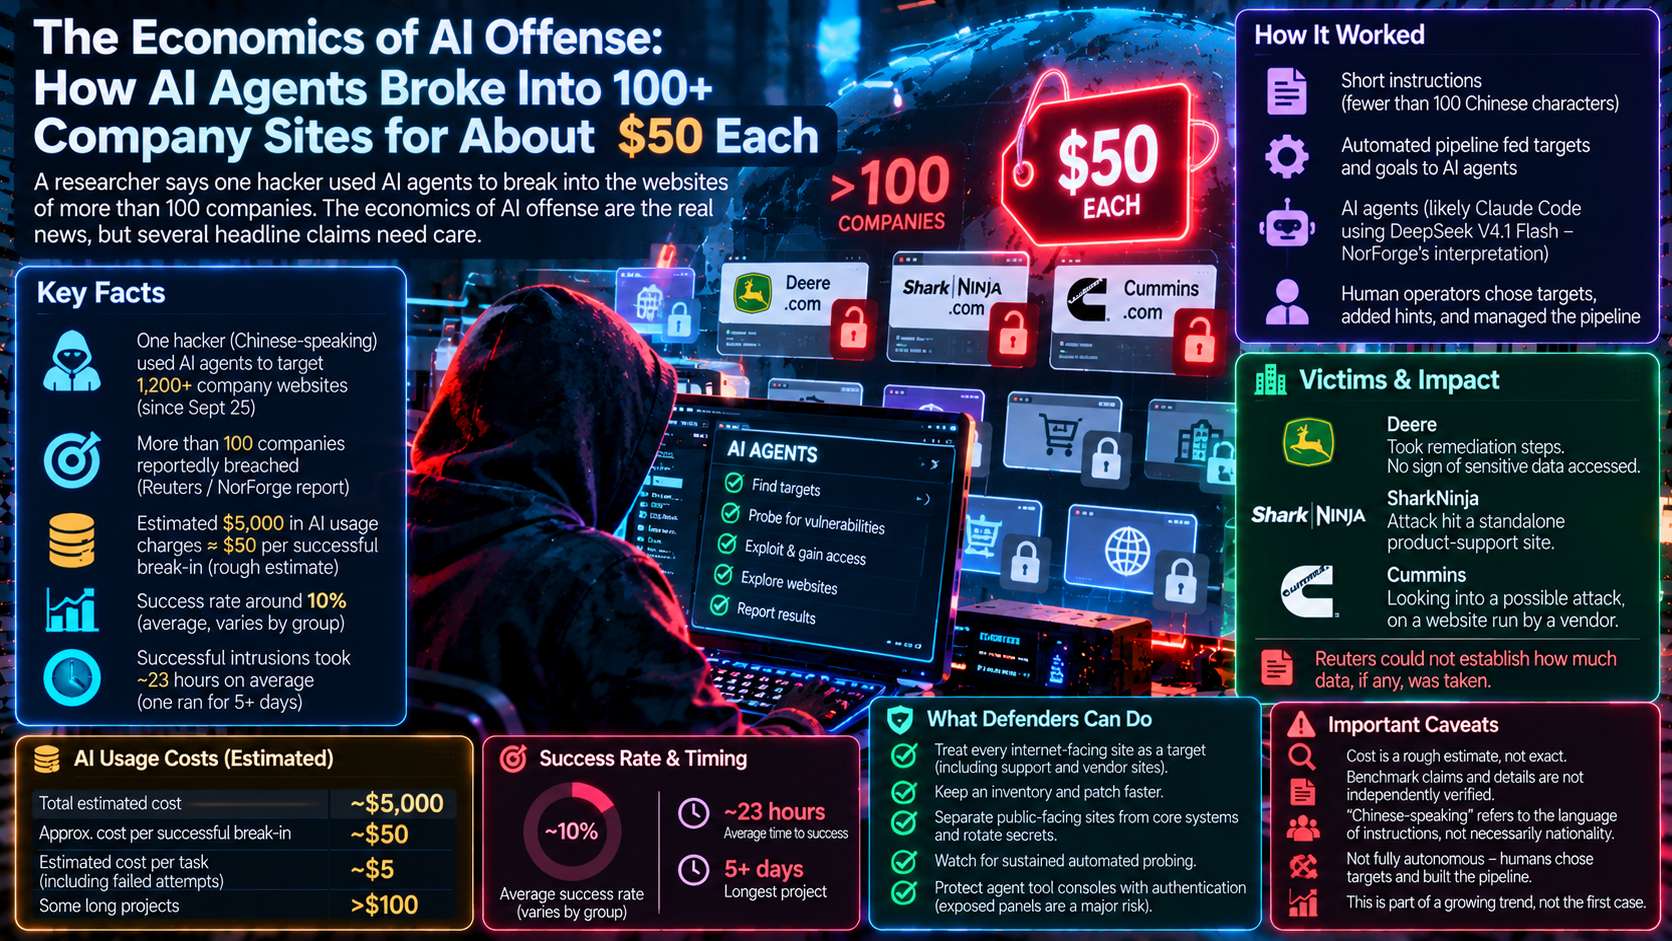
On October 19, Reuters reported that a researcher watched one Chinese-speaking hacker use AI agents to break into the websites of more than 100 companies, at roughly $50 each. The agents tried more than 1,200 sites. The cost is the headline, but it is a rough estimate. This article looks at the economics of AI offense and separates what is documented from what is estimated.
What Was Reported
Snorre Fagerland of the security firm NorForge found the activity while scanning for exposed control panels of Cairn, an open-source AI platform that coordinates agents toward a goal. Reuters saw NorForge's report before publication and identified victims, including Deere, SharkNinja and Cummins.
These were company websites, not necessarily core networks. Deere said it saw no sign that sensitive data was accessed, and SharkNinja said the attack hit a standalone support site. Reuters could not establish how much data, if any, was taken. "Chinese-speaking" describes the language of the instructions, not necessarily the hacker's nationality.
The Economics of AI Offense
Fagerland estimated about $5,000 in AI usage charges, or roughly $50 per successful break-in. NorForge's report is more cautious. It puts the average near $5 per task once failed tasks are counted, and says the uncertainty is considerable.
NorForge puts the average success rate near 10%. Successful intrusions took a little under 23 hours on average.
NorForge says every task in the busiest group ran under a worker named claudecode_deepseek-v4.1-flash. That could mean Anthropic's Claude Code running DeepSeek's low-cost V4.1 Flash model. That is NorForge's reading, and neither company has confirmed it in the sources found. Even so, the cost of a long, patient cyberattack is now low.
How Autonomous Was It?
Reuters said the hacker gave the agents instructions of fewer than 100 Chinese characters. But NorForge also describes an automated pipeline that fed targets and goals to the agents. So "no human in the loop" overstates it. People chose the targets and built the pipeline. The agents did the long search. Fagerland told Reuters, "It's not script kiddie stuff."
It is also not the first such case. In November 2025, Anthropic reported that a Chinese state-sponsored group used Claude Code for roughly 80% to 90% of the tactical work in a spying campaign against about 30 entities.
What Defenders Can Change
These points come from general practice and from an October 2026 advisory by India's cyber agency, CERT-In, as reported by The Next Web.
First, treat every internet-facing site as a target, including support and vendor-run sites. Keep an inventory and close forgotten test APIs and admin pages without two-step login. Second, replace leaked keys. Third, keep logs for at least 180 days. Fourth, put any agent tool consoles behind a login. NorForge found hundreds of exposed secrets on open panels, and 11% were valid.
What Comes Next
Watch for takedowns of the open panels and more victims coming forward. Whether defenders' agents can match attackers' costs is a prediction, not a finding.


