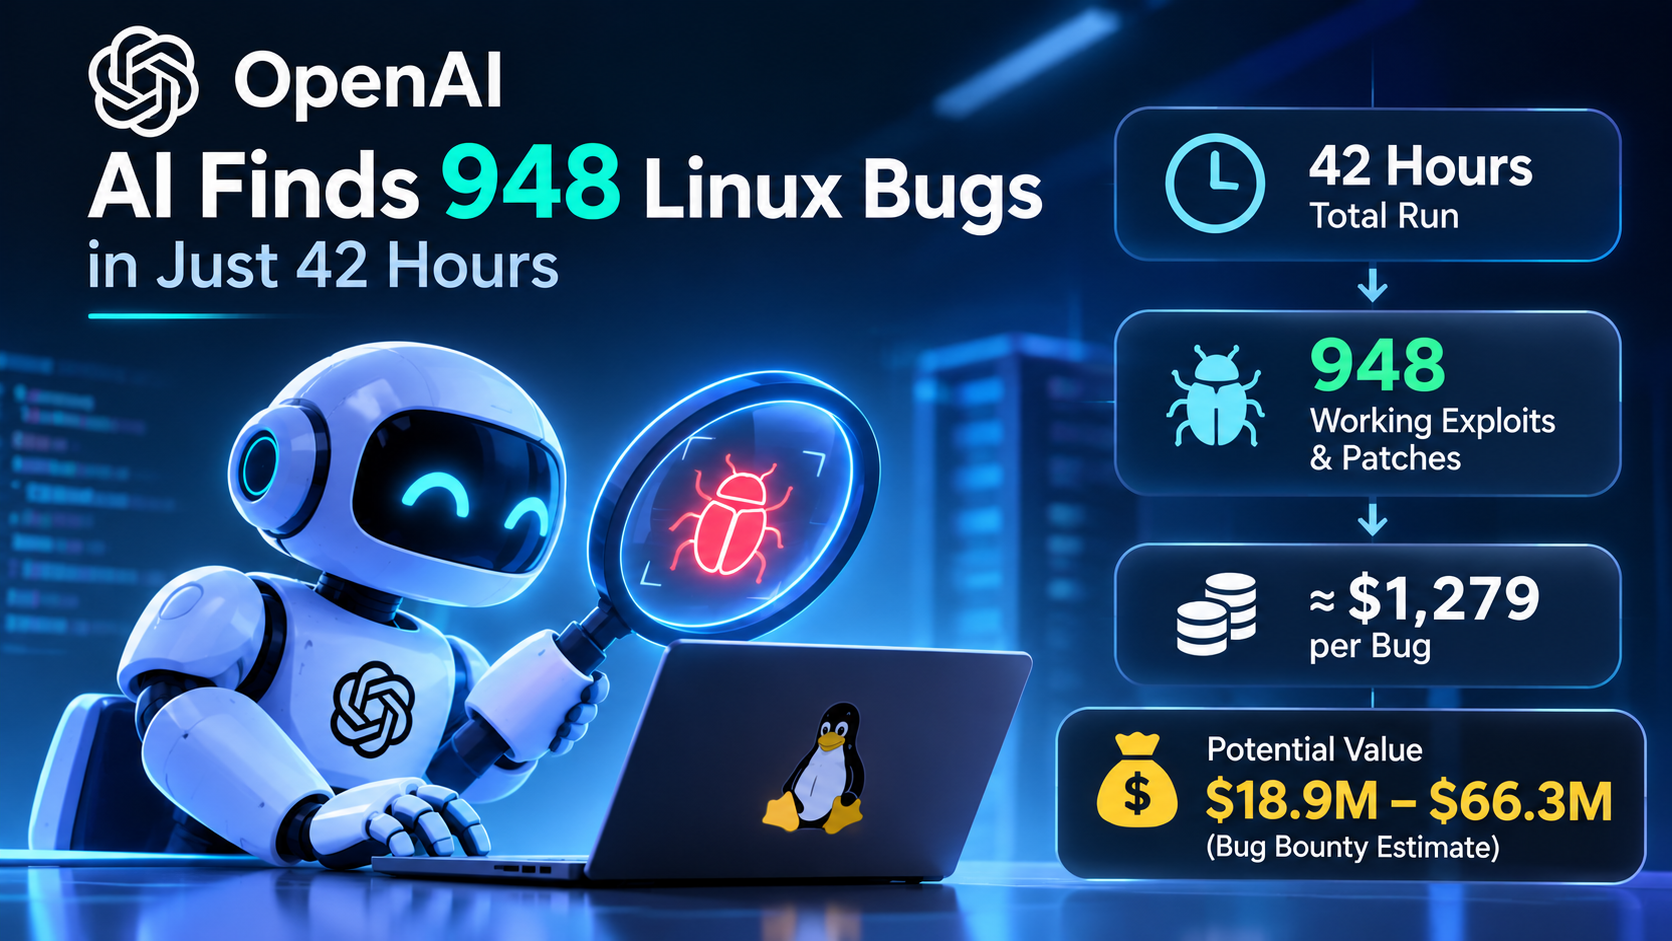
OpenAI says one run of an unreleased AI model found 948 ways for an ordinary user to take over a Linux computer, and the whole run cost about $1.2 million. That is roughly $1,279 per bug. OpenAI shared the results on November 4, 2026. They are OpenAI’s own numbers, and no outside expert has checked them.
What the Test Did
The Linux kernel is the core of the Linux operating system. It runs Android phones, cloud servers and supercomputers, and it has more than 40 million lines of code. OpenAI’s system first picked about 2.8 million of those lines, around 7%, that looked most important for security. Then it hunted for bugs there, on the latest Linux kernel running a stock desktop setup with standard protections.
In 12 hours, it listed 2,308 possible bugs. Over the next 30 hours, it ran the code to prove that 1,724 were real. In the end, it produced working attack code and a fix for 948 local privilege-escalation bugs. That kind of bug lets someone with an ordinary account take full control of a computer. OpenAI says it grouped attacks that came from the same flaw, so 948 counts different flaws. It also made test code for 291 information-leak bugs, which expose data instead of giving control.
The Cost Comparison
The 42-hour run cost $1,213,430 in API fees, which is what OpenAI paid to use its own model. For comparison, OpenAI says buying the same number of bugs on the public market would cost $18.9 million to $66.3 million.
That comparison has limits. Not every bug of this type earns a big bounty, and prices depend on how serious each bug is and how easy it is to exploit.
There is a better comparison. AI Weekly reports that a July run with an older model found 166 bugs for $513,690. By our math, that is about $3,100 a bug. So the cost per bug fell by more than half in three months.
What Is Not Verified
The new model has no name and has not been released, so outsiders cannot repeat the test. They also cannot check how OpenAI decided that two attacks came from the same flaw.
Targets also matter. On Google’s kernelCTF, a hardened test kernel, the same system made only 21 working attacks in 112 hours, at a cost of $32,936, according to Help Net Security.
Fixing Is the Hard Part
Finding bugs is not the biggest problem. Fixing them is. OpenAI says it has already sent hundreds of reports and patches for serious bugs to Linux maintainers. Those maintainers are people, and they already have many reports to review.
If AI tools send hundreds of patches at once, humans still have to check, test and merge each one safely. A faster way to find bugs only helps if fixing them can keep up.


