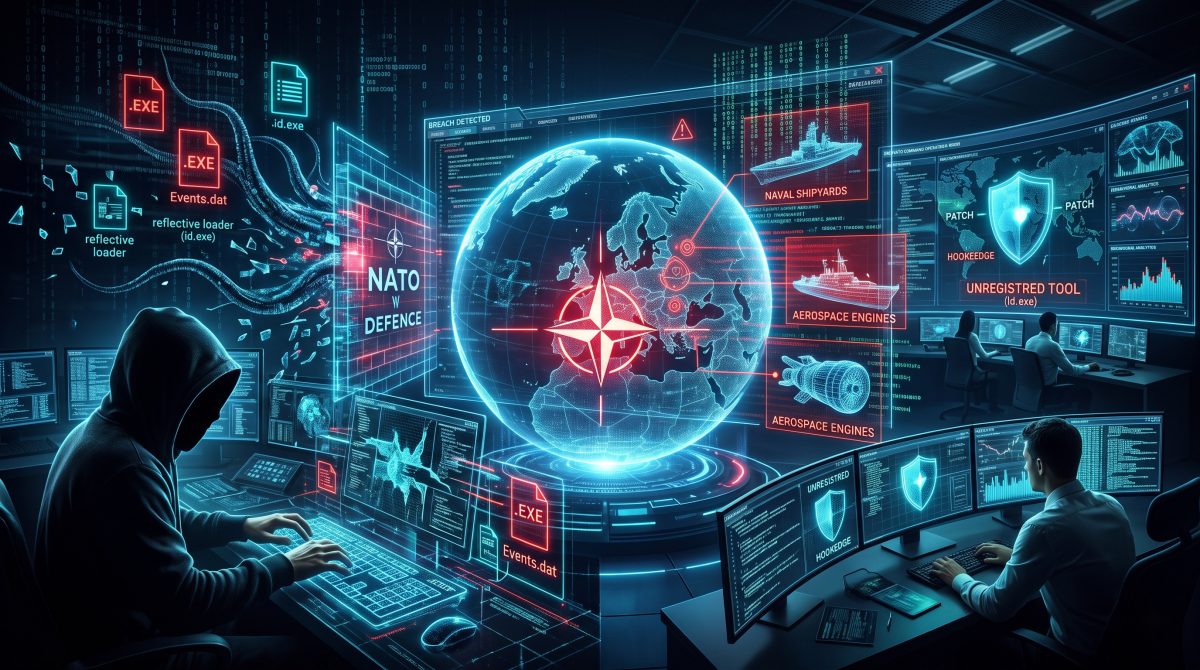
On 20 October 2026, the security firm Symantec said a hacking group linked to Russian military intelligence had breached a naval shipbuilder, a maker of military aircraft engines and a law enforcement agency in two member countries of the North Atlantic Treaty Organization (NATO). Symantec described a previously undocumented tool the attackers used. It did not name the victims or the countries, saying only that they are in Europe.
What Symantec Reported
Symantec calls the group Swallowtail. It is also known as APT28, Fancy Bear and Forest Blizzard, and APT stands for advanced persistent threat, a label for state-backed hackers. Analyst Dick O’Brien told The Record that Symantec could not tell whether sensitive data was stolen, but it is “reasonable to assume that defense-related information was the objective.” Symantec’s records run from 24 July to 24 September 2026, so the shipbuilder intrusion lasted at least two months, although researchers could not say whether access was continuous.
How the Attack Unfolded
Symantec says the breach began on 24 July, when an employee opened a malicious Word document that arrived as an email attachment. A hidden macro, a small automated script, installed a backdoor called Hookedge, which Recorded Future’s Insikt Group first described in August 2026. Over the next week, the attackers repeatedly returned to the infected computer. They stole login details using two separate techniques and opened a hidden remote-access tunnel from their own server into the company’s internal network.
The Previously Undocumented Tool
The new tool is a file named ld.exe. Symantec calls it a reflective loader, a program that unlocks an encrypted file and runs it directly in a computer’s memory. On 31 July, the attackers ran it with an encrypted file called Events.dat and a decryption key typed on the command line. Symantec recovered the key and the file name but not the file itself, so what the tool finally ran remains unknown. O’Brien told CyberScoop that ld.exe had not been publicly documented before.
Our Analysis
We checked Symantec’s report against other sources. Recorded Future, which found Hookedge first, says this group keeps refining old tools instead of building new ones, and expects more attacks on European government and diplomatic targets. A 2025 advisory from US, British and other agencies listed defence, maritime and transport firms in NATO states as targets, and warned that the group exploits business ties between companies. Our reading is that a shipbuilder and an engine maker may serve several allied forces, so one breach could matter beyond its own country. The two security firms also differ. Recorded Future expected attackers to stay on free services, yet Symantec saw sensitive work move to a dedicated server. The reports we reviewed contain no government statement.
What Defenders Can Do
Recorded Future advises blocking macros in documents that come from the internet, watching for Microsoft Edge running without a visible window, and blocking traffic to free web-testing services, called webhooks, that a company does not use. Symantec says organisations that find Hookedge traces should treat the intrusion as possibly still active. O’Brien said activity seen in September suggests the campaign is continuing. Symantec has published technical indicators for searching systems.