CERT-In Issues a Critical Alert
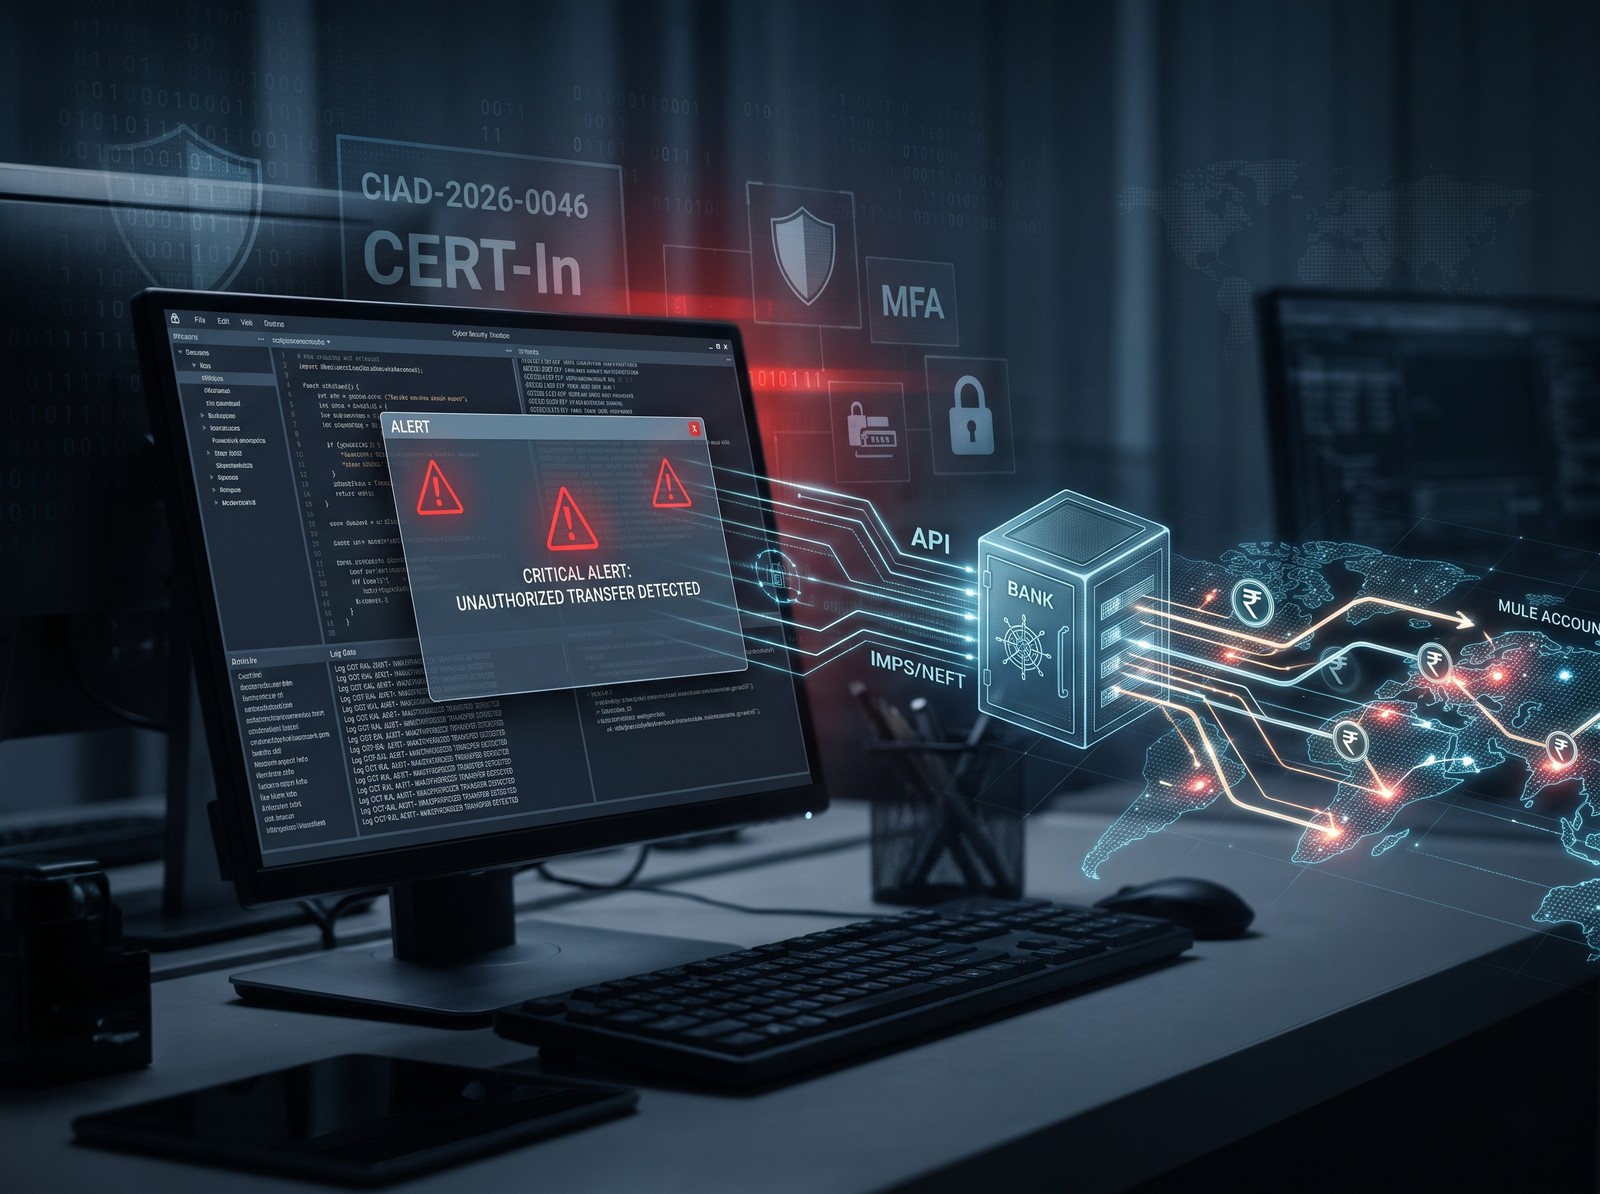
On 9 October 2026, the Indian Computer Emergency Response Team (CERT-In) issued a Critical-rated advisory about attacks on payment systems at financial companies. The advisory, numbered CIAD-2026-0046, says CERT-In has observed multiple campaigns against non-banking financial companies (NBFCs), digital lending platforms, fintech firms, payment service providers and wallet operators, all ending in unauthorised fund transfers. The advisory puts no rupee figure on the losses, and it names no victim, group or tool.
How Attackers Get In and Move Money
The advisory lists several ways in. Attackers exploit exposed internet-facing applications. They abuse deprecated, unauthenticated or unused application programming interfaces (APIs) that allow unrestricted file uploads. Some use static API tokens hard-coded in source code, or plaintext credentials in configuration files. CERT-In also lists forged commits that compromise source-code repositories, and services with no multi-factor authentication (MFA).
According to the advisory, attackers who get in set up web shells and backdoors and steal credentials for payment gateways and partner banks. They also delete or truncate logs and tamper with endpoint detection and response (EDR) tools to cover their tracks.
Why the Usual Checks Fail
What makes these attacks hard to stop is where they start. The advisory says attackers, using valid credentials, call the disbursal and fund-transfer APIs directly from the victim’s own whitelisted infrastructure. That skips the application layer entirely, so loan creation, know-your-customer (KYC) checks, beneficiary verification, balance checks and per-transaction limits never run.
The advisory says the fraudulent transactions carry dummy reference numbers that match no records and exceed per-transaction limits. Money moves fast through Immediate Payment Service (IMPS) and National Electronic Funds Transfer (NEFT) channels into mule accounts, which are bank accounts used to receive and pass on stolen money. These accounts are attacker-controlled, span multiple banks and are emptied by immediate withdrawal.
What CERT-In Says About AI and the Fix
On artificial intelligence (AI), the advisory is careful. Its Description section says analysis of the attacks indicates the “possible use of AI-assisted offensive tooling,” and its list of observed tactics repeats that hedge. It adds that the gap between first compromise and fraudulent transfer has shrunk significantly in the incidents it analysed. It confirms AI in no specific case.
CERT-In’s fixes are mostly basic. It asks firms to enforce MFA on payment platforms, admin portals and bank APIs, keep a full inventory of APIs and shut unused ones, replace long-lived static tokens with per-session authentication, and require second-level approval for all fund movement. Firms that spot suspicious activity should suspend affected APIs, preserve evidence, rotate credentials and report to CERT-In.
Our Analysis
This is our own reading, not a stated fact. The advisory reads less like a story about AI and more like a list of old security gaps: forgotten APIs, hard-coded tokens, missing MFA. If AI is involved, as CERT-In says it possibly is, our reading is that it speeds up the attackers rather than inventing new weaknesses.
We also note that the official document gives no loss total, so any rupee figure seen elsewhere needs confirmation from a regulator or police agency. Our expectation, not a confirmed fact, is that more advisories will follow, and that smaller lenders will find the controls hardest to meet.