Think of a burglar trying to break into houses along a quiet street. A normal thief tests doors one by one with a metal pin. But picture a thief with a robot tool that shakes hundreds of doorknobs in a single second. The moment it finds an open window, it slips inside without making a sound.
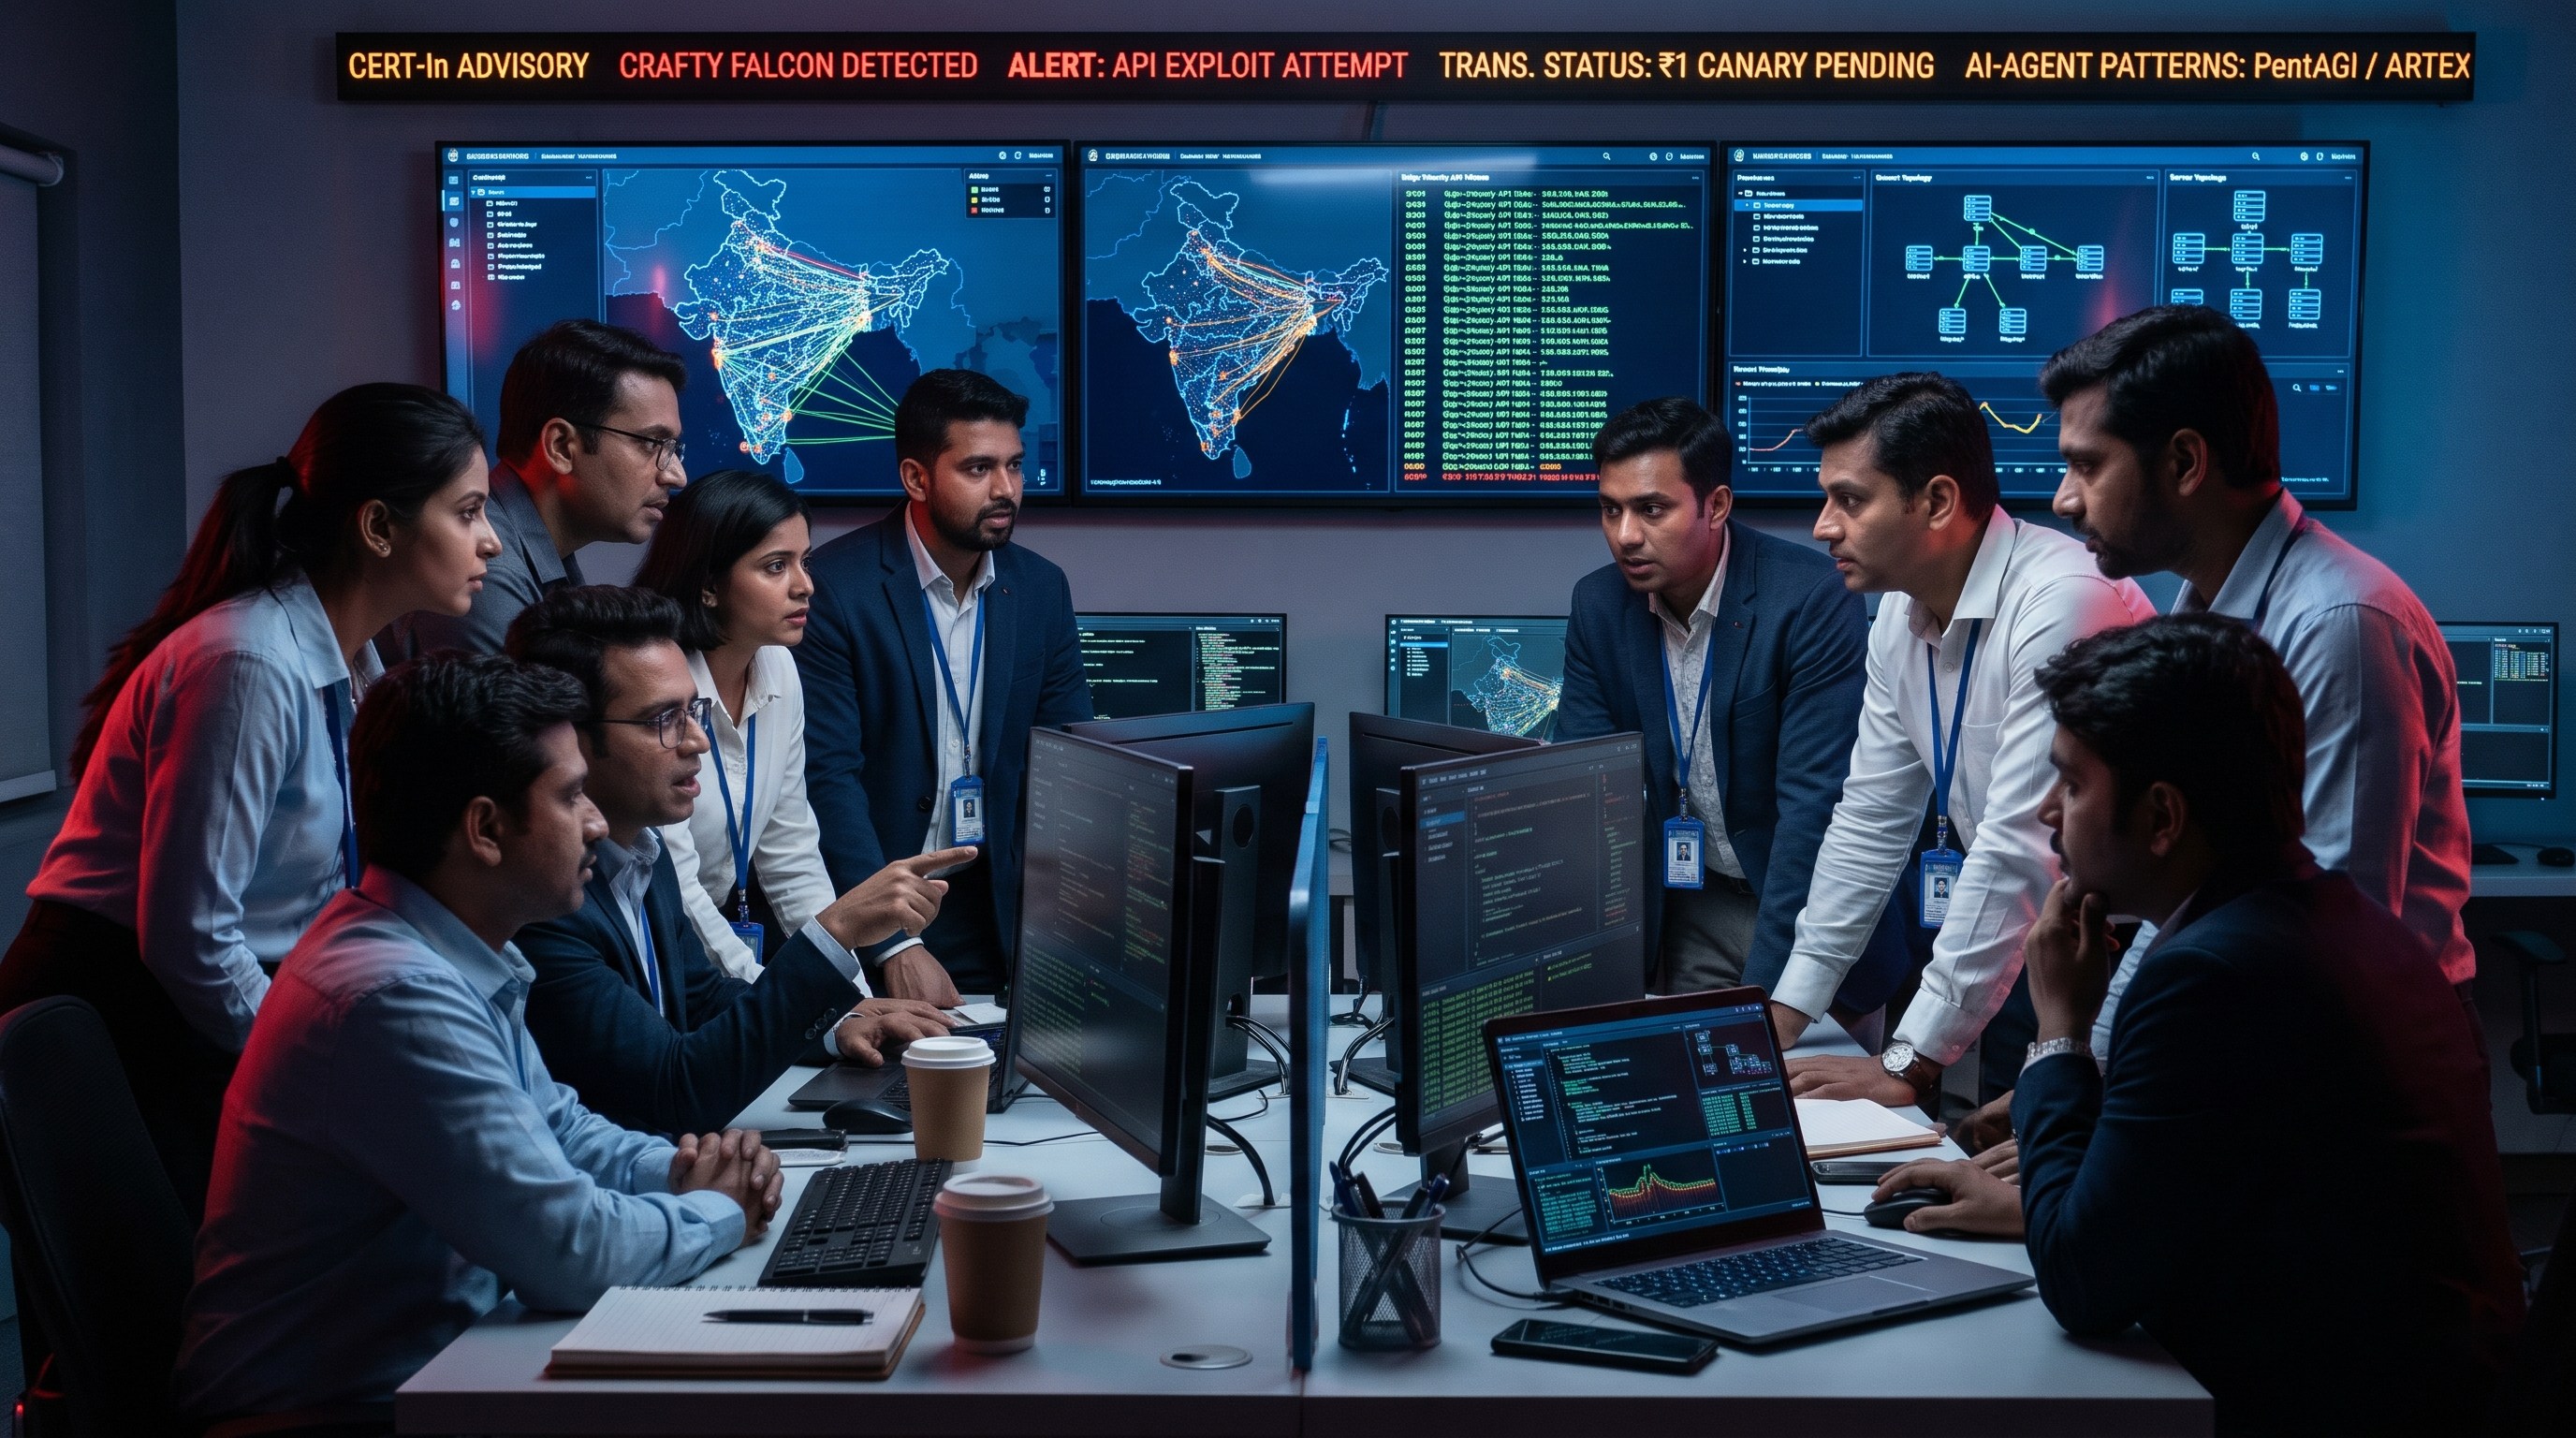
That is very close to what Indian banks and payment apps face right now. India’s main online defense agency, called CERT-In, recently posted an urgent security alert. A dangerous hacking group named CRAFTY FALCON is targeting the country’s money networks. This group wants to break into lending apps, payment gateways, and banks.
What Is Happening Right Now?
On November 4, 2026, the finance wing of CERT-In warned the country about these attacks. Criminals are running smart computer programs that test bank defenses day and night.
The hackers do not type every command by hand. Instead, they turn on automated software bots that scan thousands of bank computers to hunt for tiny software mistakes. When these bots spot a weak server, they attack immediately. The hackers also strike late on Friday nights or during long holiday weekends. They know fewer engineers are sitting at their desks during those times.
How the Attackers Break In
Mobile apps talk to banks using software bridges called APIs. An API works like a waiter at a local restaurant. You pick your favorite meal, the waiter takes your order to the kitchen, and then he brings the warm food back to your table. In banking apps, these digital waiters carry money requests back and forth between accounts.
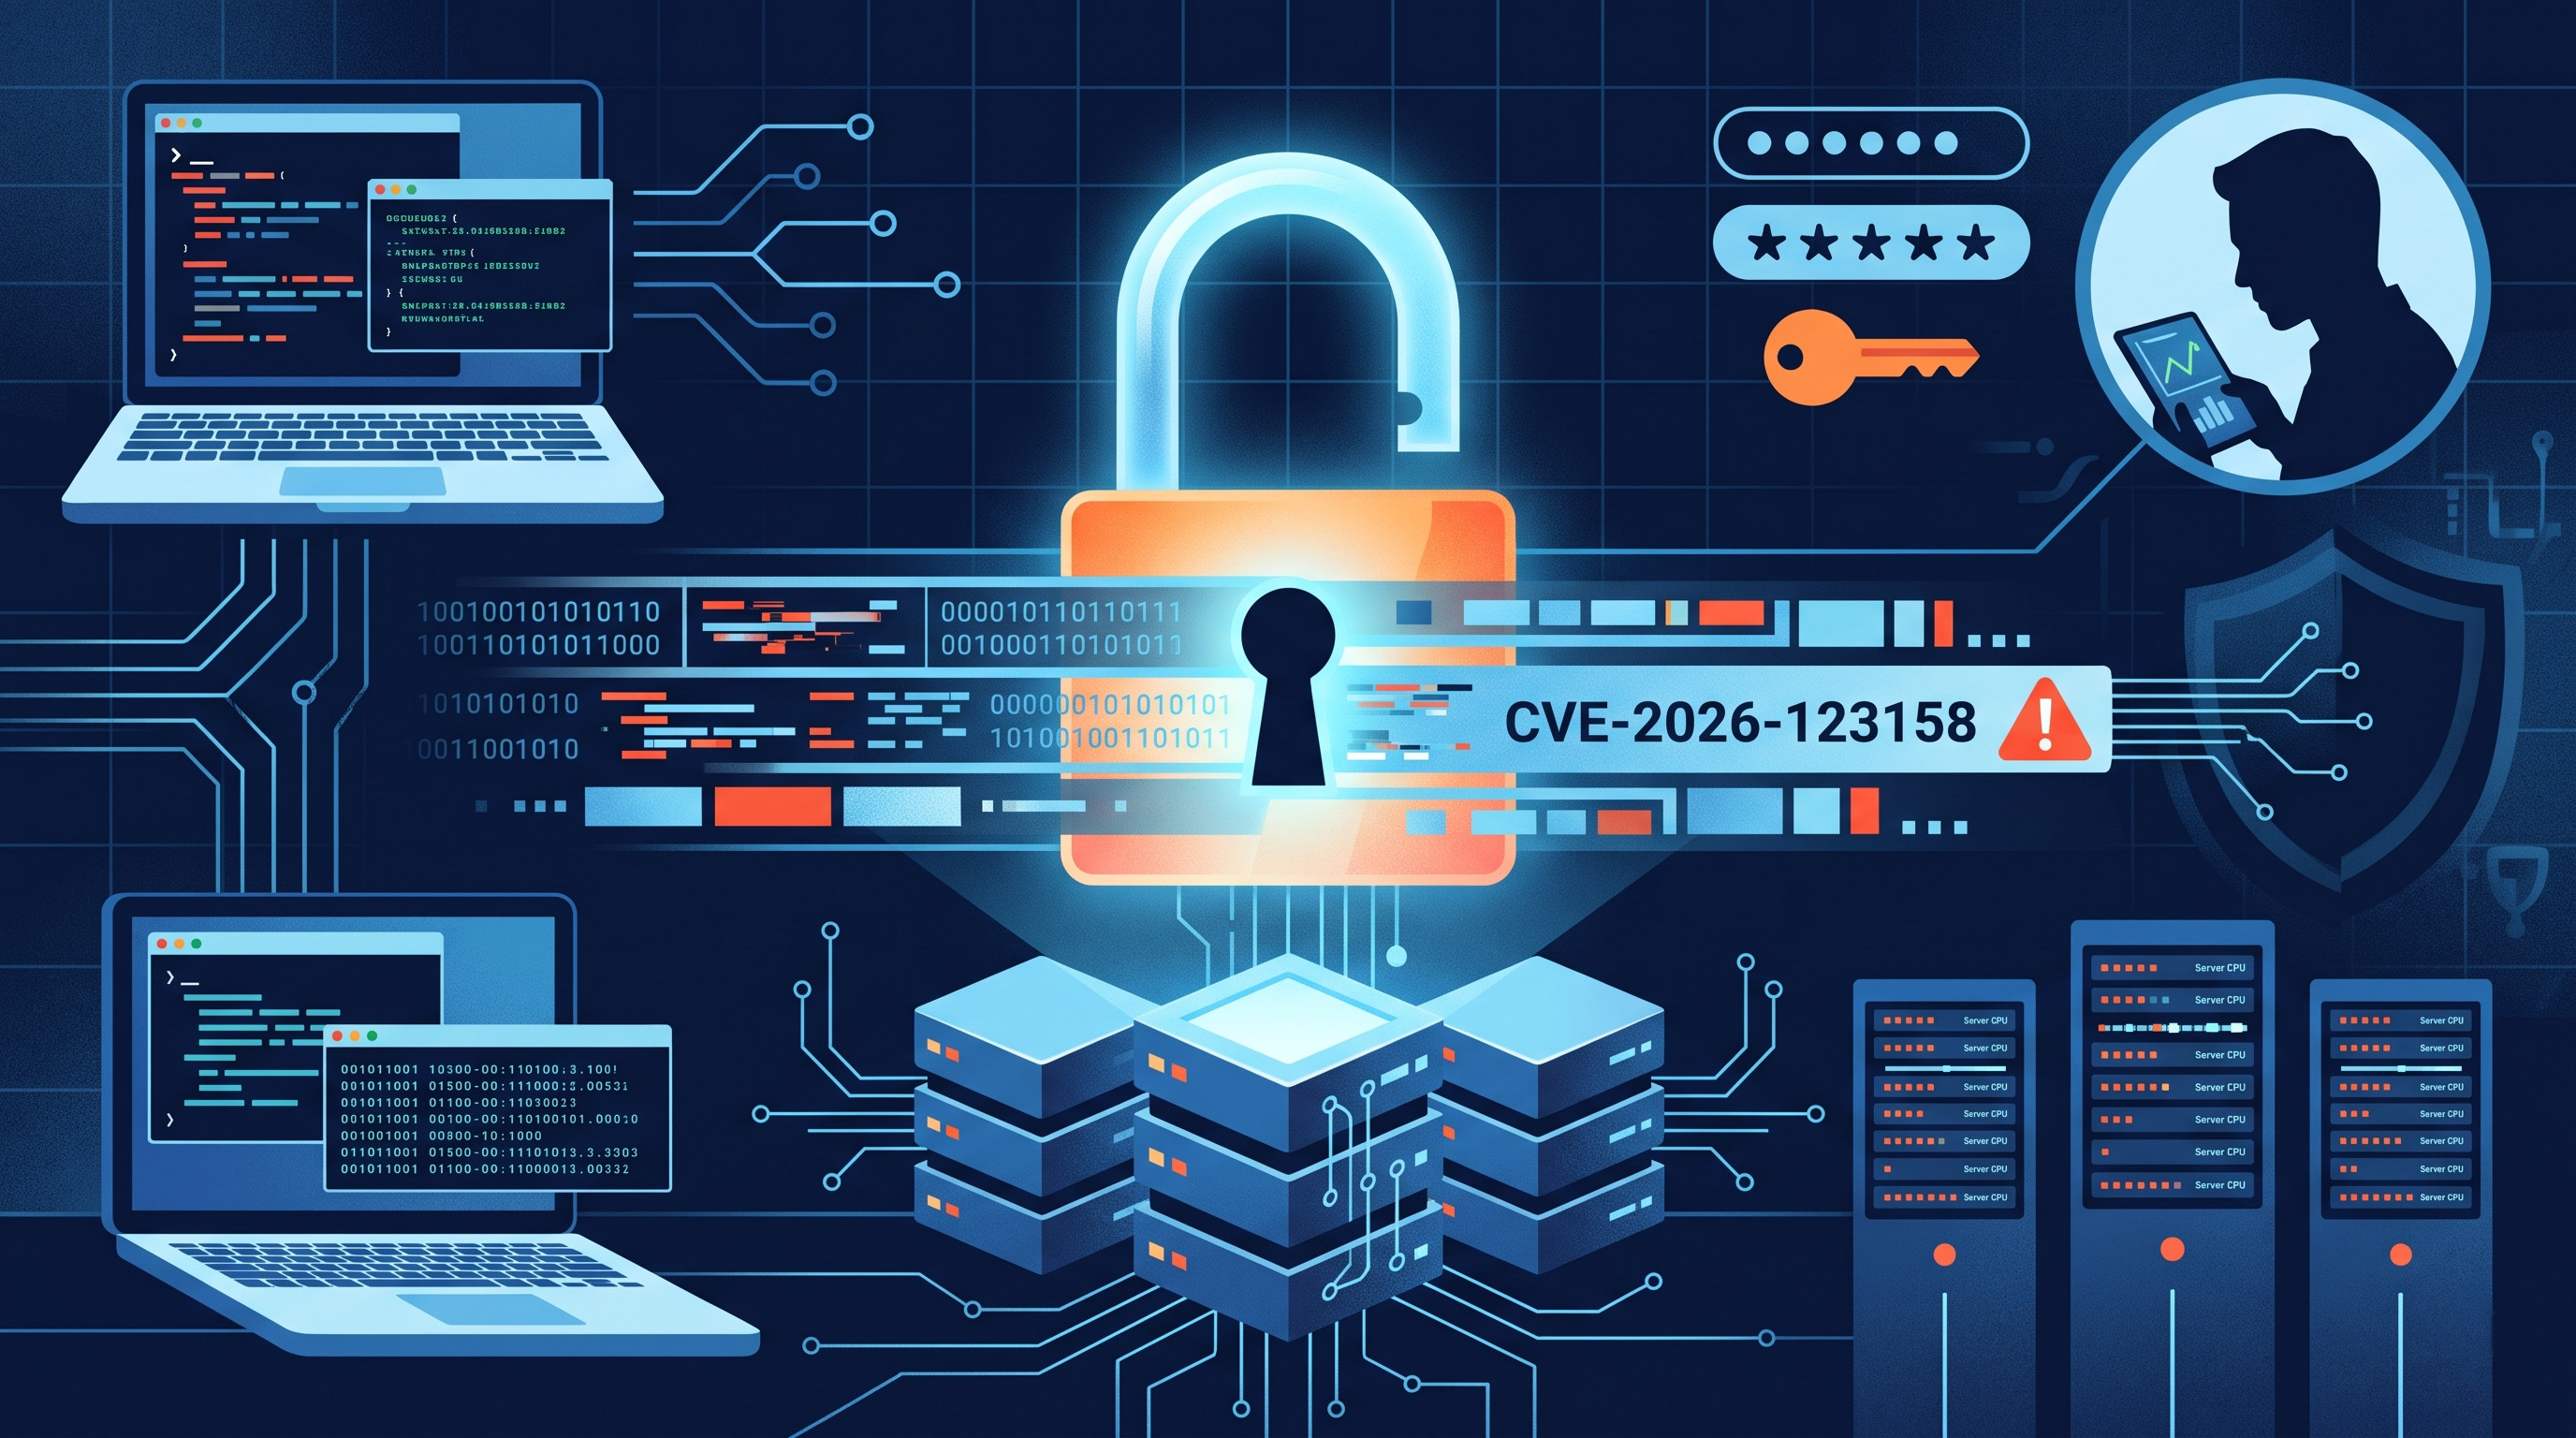
The CRAFTY FALCON group uses smart coding tools, including programs called ARTEX and PentAGI, to fool these digital waiters. The hackers often send a tiny test transfer of just one single rupee to an account first. It looks harmless, like a friend checking your UPI. But if that one rupee passes through without ringing an alarm, the tools quickly try to steal huge sums of cash.
Why This Alert Matters
Millions of Indian families use their phones every day to pay for groceries, buy bus tickets, and send money home. If thieves find sneaky backdoors into payment systems, everyday people lose peace of mind.
CERT-In noticed another troubling pattern. Some companies thought they fixed their computer bugs after an early warning, but the hackers broke back inside days later. The attackers simply discovered forgotten passwords and old testing computers that staff forgot to disconnect.
What Companies Must Do Next
Stopping these attacks takes real discipline. The software programs the hackers use were originally built by good computer researchers to test internet security. But in bad hands, those same tools become digital weapons. CERT-In says banks must keep security teams at their posts through weekends, demand that two managers approve large money payouts, and keep experimental computers completely locked away from real customer data.