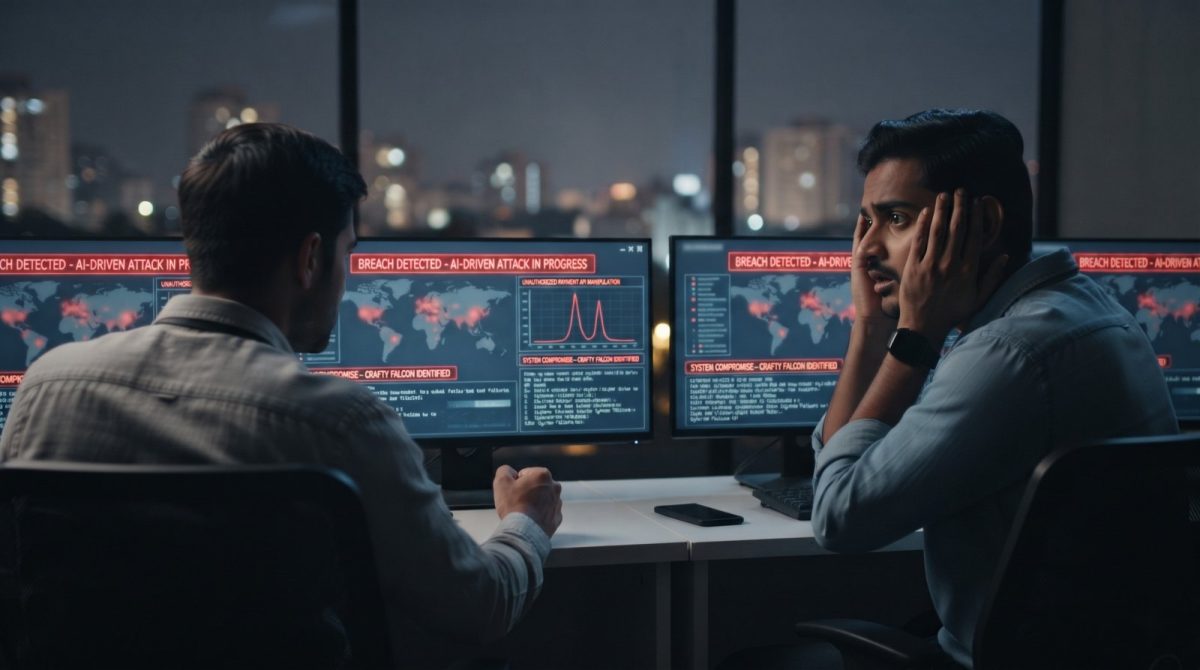
India’s cyber agency, CERT-In, says AI-powered cyberattacks are hitting Indian financial companies. On 4 November 2026, it put out advisory CIAD-2026-0058 and rated the threat Critical and ongoing. Think of a burglar who copies your house key and walks in through the front door. The attackers use a company’s own payment systems to move money out.
What happened
This advisory follows an earlier alert, CIAD-2026-0046, from 9 October 2026. CERT-In’s finance team, CSIRT-Fin, named the attacker CRAFTY FALCON and called it an AI-assisted financial threat actor. The victims include lenders, fintech companies, payment firms and crypto exchanges.
Some companies had already fixed their problems and still got attacked again. The attacks also happened on holidays and weekends, when fewer people are watching the systems. CERT-In did not name any victims or give a loss figure. It also didn’t say which recent bank attacks are linked to this group, or who is behind it.
How the attacks work
The advisory says attackers often get in through test servers that are open to the internet. It’s like a side door into a bank. After that, shared passwords or tokens can lead them to the real systems.
Some misused cloud tools to run commands without looking suspicious. Others copied a company’s app code and sent fake requests to its payment API. A payment API is the digital doorway that lets software ask for a money transfer. Before moving big amounts, they sent tiny test payments, like Rs. 1.
The AI tools
CERT-In names four public AI tools: the ARTEX family, PentAGI, Cairn and CyberStrikeAI. It says they can run a whole attack on their own, write lots of custom scripts quickly, and change their plan based on how the target reacts.
CERT-In says the huge number of near-identical scripts fits with AI-written code. That is a careful statement, not proof. Business Standard reports that researchers link at least two of the tools to China, but CERT-In doesn’t say who is behind the attacks.
What comes next
CERT-In gives no forecast. It only says the campaign is active and growing, and that attackers often keep the same methods even when their signs change. It suggests decoy systems to trap automated attackers, constant monitoring, and extra staff with lower alert limits on weekends and holidays. No source says ordinary customers have been hurt.
My analysis
This part is my own opinion, not CERT-In’s. Public tools make these attacks easier for people with less skill, and small lenders may find it hard to watch their systems all day and night. One fix also doesn’t seem to be enough, because the attackers came back. Cyble points out that weak basics, like hardcoded tokens and missing multi-factor login, were already in the October advisory. So AI may be making attacks faster more than creating new weak spots.
If you build a finance app, keep test servers separate, check every request on the server, and watch weekends. When attackers never stop, steady basics matter more than any single new tool.