What CERT-In published and who it covers
CERT-In’s guidelines page lists the document as CISG-2026-04, dated 4 November 2026. The PDF says a CERT-In sub-group on cybersecurity audits wrote version 1.0. The rules cover AI systems that organisations in India build, buy or run. They also cover systems that handle Indian data or serve Indian users. College research AI, simple rule-based automation and personal-use AI are left out.
How the risk tiers work
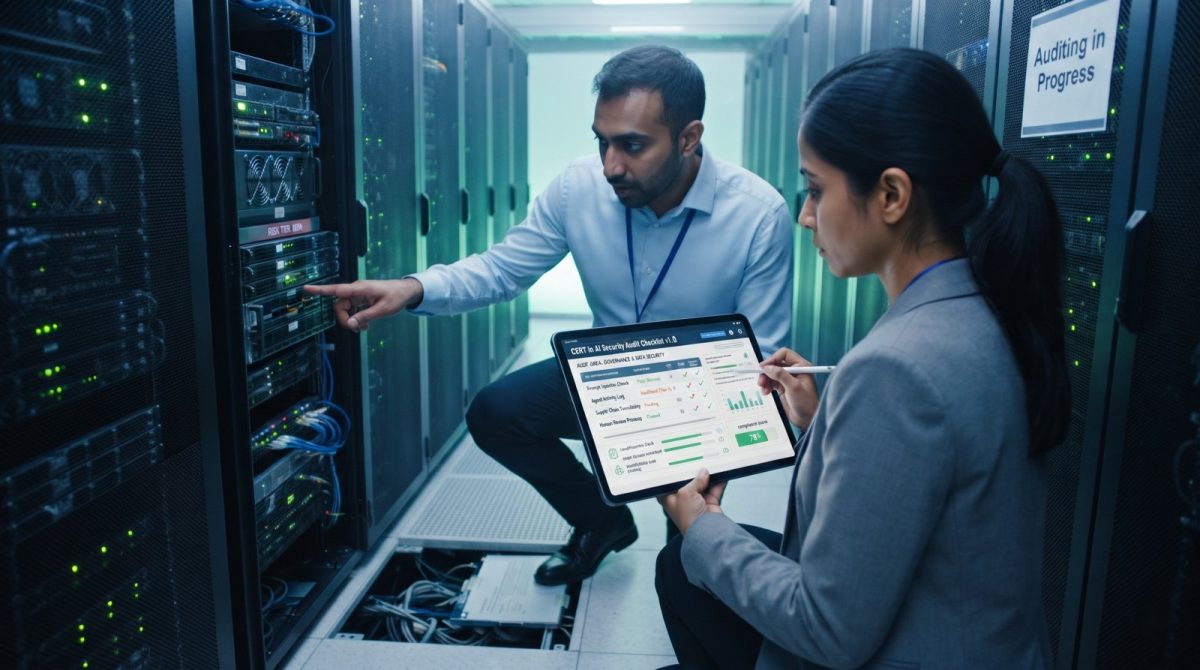
The PDF checks every AI system on eight points, like how much harm a failure could cause and how private its data is. Each point gets one to four marks. A total of 8 to 12 means Low risk, 13 to 19 is Moderate, 20 to 26 is High and 27 to 32 is Critical. A Moderate system needs an outside audit at least once a year by an auditor CERT-In has approved. A Critical system needs that audit and nonstop monitoring. The PDF lists nine audit areas.
The new threats behind the rules
The PDF adds extra checks for generative AI tools and AI agents, which are programs that act on their own. It names prompt injection, which means hiding instructions that trick an AI. CERT-In chief Sanjay Bahl told MediaNama that advisory CIAD-2026-0049, issued on 15 October 2026, describes AI agents getting into live systems without permission. MediaNama adds that AI incidents covered by the rules must be reported to CERT-In within six hours.
What could happen next
The sources say little about the future. Bahl says that if AI agents become common, defence has to work at machine speed. He says CERT-In will keep issuing advisories, and that AI bills of materials, which are lists of an AI system’s parts, will matter more. The PDF already names banking, healthcare and manufacturing as users of AI. MediaNama reports that people hurt by an AI decision should be able to ask for a human review, where this applies. No source I opened gives numbers for the market or jobs, so the business impact isn’t known yet.
My thoughts
This part is my own thinking, not CERT-In’s. Say a system scores 2 out of 4 on all eight points. That adds up to 16, which is Moderate, so it may need a yearly outside audit. The PDF says the higher group applies if the auditor and the company disagree. It also keeps systems built on other firms’ AI models inside the rules. So buying an AI service doesn’t pass the duty to the seller.
Bahl says few organisations keep full records of what their AI agents do, so record-keeping may be the first gap. The pages I opened give no audit costs.
These rules turn a vague worry about AI safety into a checklist with auditors and time limits. What matters now is whether organisations follow them honestly, and whether small firms get clear help.