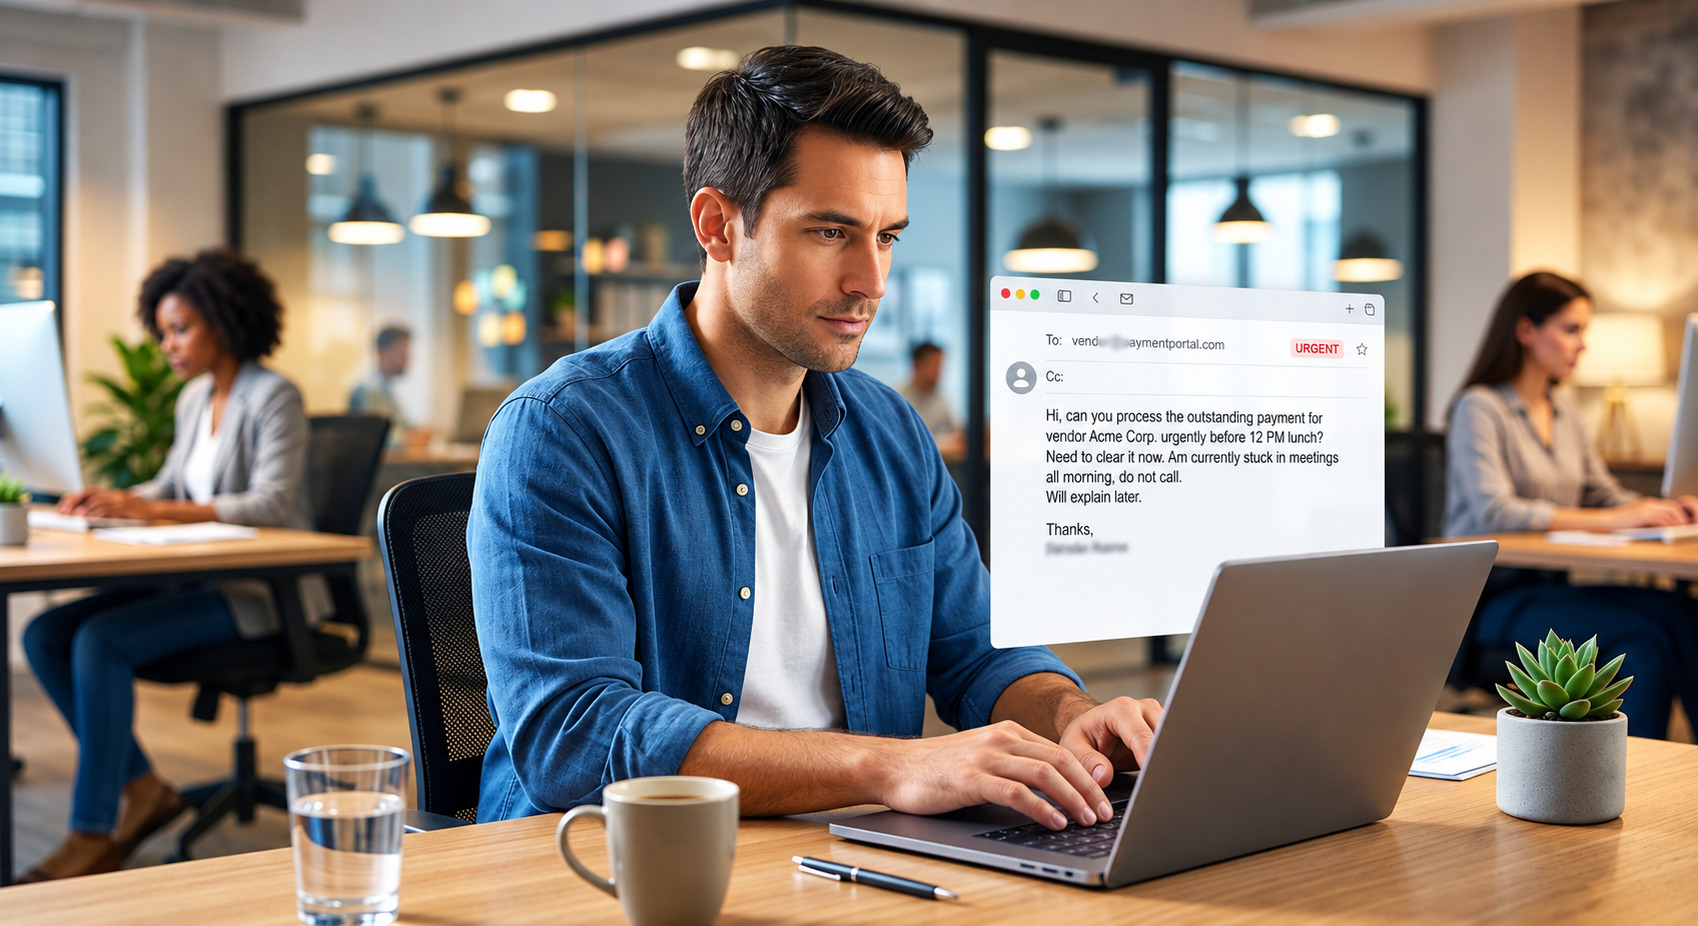
Picture an email from your department head, 10:40 on a Tuesday. It’s short, a little curt, and ends with her usual “Thanks, will explain later.” She wants a vendor payment cleared before lunch and says not to call because she’s stuck in meetings.
Nothing looks off. But she didn’t send it.
How attackers pick up a writing style
Copying how someone writes used to be slow. You needed a stack of their emails and some patience. Now an attacker can paste a few public things into a chatbot, say a LinkedIn update, a talk transcript or a company blog post, and ask it to write a short payment request in the same tone. If they’ve got into a real inbox, they have even better material.
Before writing, they usually do some homework called OSINT, short for open-source intelligence. It just means collecting whatever is public: who reports to whom, which vendor gets paid on which date, what project is running late. AI tools can do that collecting and the writing in one go.
What the studies actually found
IBM’s X-Force team ran a test in 2023 on more than 800 employees at a healthcare company. One phishing email was written by their own social engineers, the other by ChatGPT from a few prompts. People clicked the human one 14% of the time and the AI one 11%, and more people reported the AI email as suspicious. Where the AI won was time. IBM says it took about five minutes, against around 16 hours for the human team.
A 2024 academic study used 101 volunteers. Fully automated AI emails got clicked 54% of the time, the same as emails written by human experts, while a generic email got 12%. That is where the claim that AI phishing is “four times better” comes from, but it was a small study and the AI only matched the experts, it didn’t beat them. AI models have also improved since 2023, so neither result should be treated as final.
So the realistic picture is that AI isn’t writing better scams than a skilled human. It’s writing them for almost nothing. Tailored attacks used to be worth the effort only for big targets, and that is changing.
Why the boss email is the risky one
The technical name is business email compromise, or BEC. The attacker pretends to be a senior person or a supplier and asks for a payment or new bank details. Often there’s no link or attachment at all, so there is nothing for a spam filter to catch.
For India, an ESET survey from 2026 says 85% of Indian organisations faced at least one AI-related threat in the last year, and 48% saw AI-written phishing or impersonation. It’s a vendor survey with self-reported answers, so treat it as a rough direction. CERT-In, India’s national cyber agency, also named executive impersonation and BEC in an AI-threat blueprint it released on 25 May. The blueprint is advisory, so organisations aren’t required to follow it.
What still gives these emails away
Writing style isn’t a useful check anymore, so look at other things.
The request itself. A changed bank account, a rush payment, gift cards, anything outside the normal process should slow you down, however natural the tone is. Pressure and secrecy (“don’t call, just do it”) make it worse.
The sender address. Click on the name and read the full address. Look for small swaps like “rn” in place of “m”.
Specific details. In IBM’s test the human team did better partly because it mentioned something real from inside the company. The chatbot stayed general. If an email avoids things only your boss would know, that’s worth noticing.
The simplest defence is checking through another channel. Phone the person on a number you already have, or message them on the company chat. Many companies also require two people to approve any change in payment details. DMARC, which lets a domain owner tell other mail servers to reject emails faking their address, stops spoofed addresses but won’t help if a real account has been hijacked.
People were told for years to watch for bad spelling and awkward grammar. That doesn’t work well anymore. It’s better to ask whether your boss would really ask you for this, and in this way.